How Cybersecurity Gaps Develop as a Business Grows


Growth is usually something a business works hard to achieve.
More customers. More employees. New opportunities. Perhaps another location, a larger office, or new technology that makes everyday work easier.
Each change makes sense on its own.
A new employee needs access to company information. A department introduces software to improve productivity. An outside contractor needs to collaborate with the team. A new location requires connectivity to the same business systems.
The business keeps moving forward.
But somewhere along the way, an important question can become difficult to answer:
Has the way we protect the business kept up with the way the business now operates?
This is where cybersecurity gaps can begin to develop.
Not necessarily because someone ignored security or made a particularly bad decision. Often, the company has simply changed faster than its technology practices, responsibilities, and safeguards.
Understanding how that happens is the first step toward preventing small oversights from becoming larger business problems.
The Business You Secured Is No Longer the Business You Have
Think about how technology is often managed when a company is small.
There may be a handful of employees, a few essential applications, and one person who understands most of the systems. Decisions are relatively straightforward because the business is still manageable through direct knowledge and personal involvement.
The owner knows who works there, which suppliers have access, and which systems are important.
As the company grows, that familiarity becomes harder to maintain.
Employees join different departments. Managers begin making their own technology decisions. Outside specialists become involved. Information moves between more applications, devices, and locations.
The original security arrangements may still be in place.
The difficulty is that those arrangements were designed around an earlier version of the organization.
A practice that worked reasonably well for ten employees may not provide the same visibility or control when the company has fifty.
The question is not whether the original decisions were wrong.
It is whether they still fit the business today.
Growth Creates Connections That Are Easy to Overlook
Every new business relationship introduces some form of connection.
An employee may need access to financial records. A marketing agency may require access to company accounts. An accounting firm may exchange sensitive documents. A software provider may integrate with existing applications.
These connections support legitimate business activities.
They also expand the number of people, systems, and organizations involved in handling company information.
Consider a business that gradually adopts several cloud applications.
One application manages customer relationships. Another handles accounting. A third supports project management. Additional tools help employees communicate and share files.
Each application may have its own user accounts, administrative settings, access permissions, and security features.
Over time, the company may find that nobody has a complete view of how these systems connect or who is responsible for managing them.
The problem is not necessarily the number of applications.
It is the growing distance between how the business uses technology and how well that technology is understood and controlled.
A useful starting point is to identify which systems are essential to daily operations, who uses them, and which outside organizations can reach them.
That exercise often reveals questions worth investigating before they become urgent.
When Responsibilities Become Unclear
One of the less visible effects of business growth is the way responsibilities change.
In a smaller company, a business owner may personally approve new software, employee access, and technology purchases.
Later, those decisions become distributed.
A department manager approves an application. Human resources handles employee onboarding. An outside IT provider manages certain systems. A software vendor administers another part of the environment.
Each person may be doing exactly what the business expects.
Yet important responsibilities can fall between them.
Who confirms that a departing employee no longer has access to every relevant application?
Who reviews the permissions granted to an outside contractor?
Who decides whether a newly purchased system meets the company's security expectations?
Who verifies that an important business application is included in recovery planning?
Without clear ownership, people may reasonably assume someone else is handling these tasks.
That assumption can persist for months or years because nothing has happened to challenge it.
One practical improvement is to establish responsibility for important systems and decisions.
This does not mean every company needs a dedicated cybersecurity department.
It means someone should be able to explain who approves access, who maintains the system, who reviews its configuration, and who takes action when circumstances change.
Access Does Not Always Change When People Do
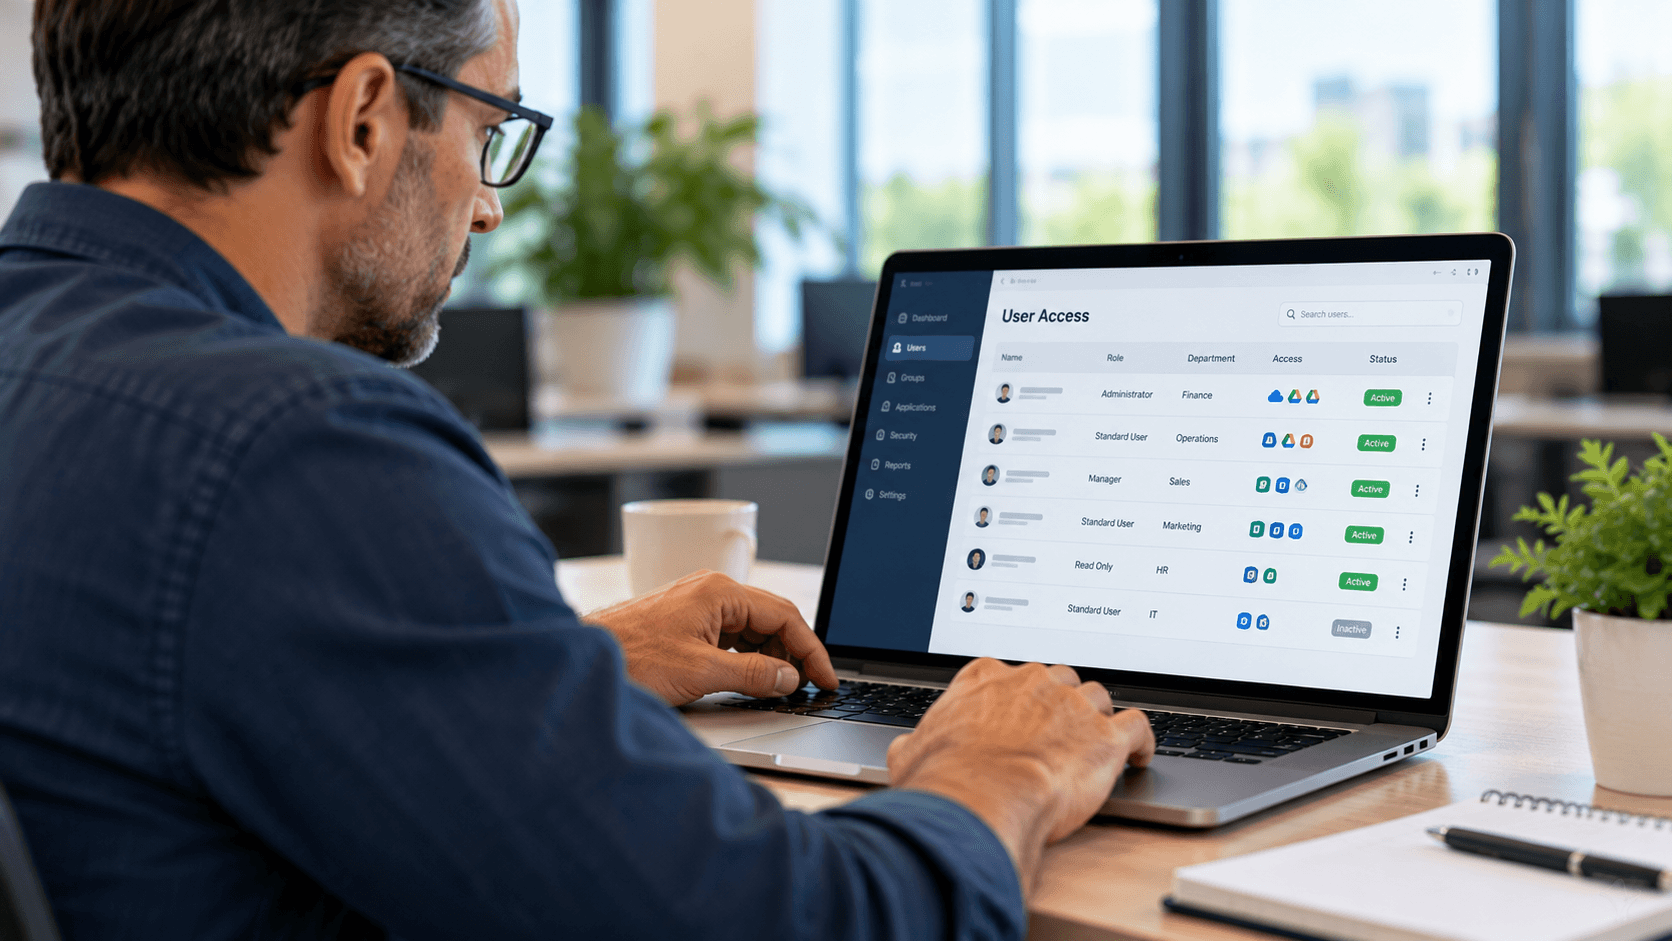
Employee and contractor access deserves particular attention because business relationships rarely remain static.
Someone joins the company in one role, takes on additional responsibilities, moves to another department, and eventually leaves.
At each stage, their technology needs may change.
New permissions are often added because they are necessary to complete the next assignment.
Removing permissions that are no longer needed can receive less attention.
The same problem applies to outside vendors, temporary workers, and business partners.
A contractor may receive access for a specific project. When the work ends, the business relationship changes, but the account or permission may remain active.
Over time, the organization can accumulate access that no longer reflects current responsibilities.
This creates unnecessary exposure, particularly when permissions allow users to reach sensitive information or make administrative changes.
The solution begins with treating access as something that must be managed throughout a business relationship, not simply granted at the beginning.
That means considering five stages:
- Authorize: Decide what access is appropriate and who approves it.
- Enable: Provide the access required for the person's responsibilities.
- Use: Make legitimate work possible without unnecessary restrictions.
- Review: Revisit permissions when roles, projects, or circumstances change.
- Withdraw: Remove access when it is no longer required.
These principles apply whether a business has a small internal team or works with multiple outside organizations.
For a closer look at this challenge, see Who Really Has Access to Your Business Information?.
When Technology Is Added Without Considering the Whole Environment
Businesses rarely build their technology environments all at once.
Systems are usually introduced over several years in response to immediate needs.
An accounting application solves a financial management problem. A cloud service improves collaboration. New networking equipment supports an office expansion. Another product helps protect company devices.
Each purchase may have been justified.
But individually reasonable decisions do not automatically produce a well-coordinated technology environment.
Different systems may have different authentication requirements, administrative procedures, monitoring capabilities, and recovery arrangements.
Some may depend on services that employees barely notice until those services become unavailable.
The business can end up with multiple layers of technology but limited visibility into how they operate together.
For example, a company might have reliable backups for its primary server while assuming that information stored in separate cloud applications is covered by the same recovery process.
Whether that assumption is correct depends on the applications, configurations, and actual backup arrangements.
Similarly, installing security software on employee computers does not automatically address inappropriate access permissions, weak account recovery practices, or unmanaged third-party connections.
The important question is not simply which tools the company owns.
It is whether the protections work together to support the way the business actually operates.
That requires looking beyond individual products and understanding the relationships between systems.
Growth Changes the Consequences of a Technology Problem
A technology issue that was manageable when a company was smaller may have a very different impact after several years of growth.
Consider a business application used by only two employees.
If the application becomes unavailable, the disruption may be limited to a small part of the organization.
Now consider the same application after it becomes central to customer service, purchasing, scheduling, and financial reporting.
The technical problem might be identical.
The business consequences are not.
More employees may be unable to work. More customers may be affected. Important decisions may be delayed because the information needed to make them is unavailable.
Cybersecurity risk changes in a similar way.
As a company grows, it may hold more customer information, process more transactions, rely on more outside services, or face additional contractual expectations.
The value and sensitivity of the information being handled can change.
So can the business's tolerance for interruption.
This is why cybersecurity planning should not be separated from operational planning.
Business owners need to understand which systems and information matter most, what would happen if they became unavailable or compromised, and which activities would need attention first.
Those answers help determine where protection and recovery efforts should be concentrated.
Why Buying More Security Tools Is Not Always the Answer
When a business becomes concerned about cybersecurity, purchasing another product can feel like a practical response.
Sometimes additional technology is necessary.
But a new tool cannot automatically correct unclear responsibilities, outdated permissions, undocumented systems, or assumptions that have never been tested.
In some cases, adding another product creates additional administrative work without resolving the original problem.
Before making a purchase, it helps to ask what the business is actually trying to improve.
Is the concern that former employees may still have access?
That important systems are not being monitored?
That backups have not been tested?
That nobody knows which outside providers can access company information?
Or that the business has grown without revisiting its technology practices?
These are different problems.
They may require different responses.
A business that cannot identify who administers its critical applications may benefit more from clarifying ownership and reviewing permissions than from immediately adding another security product.
Likewise, a company concerned about operational disruption may need to verify its recovery arrangements before investing in additional preventive measures.
The goal is not to minimize technology investment.
It is to make sure each investment addresses a meaningful business risk.
How to Recognize When Security Practices Have Fallen Behind
A growing company does not need to wait for an incident to reconsider its cybersecurity arrangements.
Certain everyday observations can suggest that a review would be worthwhile.
For example, managers may be uncertain about which applications employees use. New accounts may be created without a consistent approval process. Departing employees may rely on informal reminders to have access removed.
Perhaps different departments purchase software independently, or important recovery procedures exist only in one person's knowledge.
None of these observations proves that the business has experienced a security failure.
They do, however, identify areas where responsibilities and expectations may need clarification.
A useful review can begin with a few practical questions:
- Which systems and information are most important to our daily operations?
- Who is responsible for approving and managing access to them?
- What has changed in our workforce, applications, vendors, or locations?
- Which protections have actually been checked rather than simply assumed to be working?
- If an important system became unavailable tomorrow, who would coordinate the response?
The answers do not need to produce a perfect technology plan immediately.
They should help the business identify its most important uncertainties and decide what deserves attention first.
Security Needs to Evolve Alongside the Business
Cybersecurity is often treated as a project with a beginning and an end.
A company installs protective software, configures accounts, establishes policies, and considers the work complete.
But the business continues changing.
New employees arrive. Responsibilities shift. Applications are replaced. Suppliers change. Customer expectations evolve.
A security arrangement that was appropriate last year may need adjustment today.
This does not mean every change requires a major technology project.
It means that growth should trigger thoughtful questions about the environment supporting the business.
When a new department is created, consider how access will be managed.
When a new application is introduced, determine who will administer it and how its information will be protected.
When a vendor relationship ends, confirm that access and responsibilities have been addressed.
When a critical process becomes more dependent on technology, revisit the consequences of an interruption.
These are manageable conversations when they happen as part of normal business planning.
They become much more difficult when postponed until something stops working.
A Growing Business Needs a Clearer Picture, Not Just More Protection
The most important cybersecurity gaps are not always obvious technical weaknesses.
Sometimes they are unanswered questions.
Who owns this system?
Why does this account still exist?
Is this information protected the way we think it is?
Would we know what to do if this application became unavailable?
These questions become more important as a business grows because more people and activities depend on the answers.
Growth itself is not the problem.
The challenge is allowing technology responsibilities and safeguards to remain unchanged while the organization around them becomes more complex.
A business does not need to eliminate every possible risk to make meaningful progress.
It needs a realistic understanding of its environment, clear responsibility for important decisions, and a practical way to revisit those decisions as circumstances change.
At Nivo 5, we believe technology should support business growth without introducing unnecessary uncertainty into everyday operations.
If your company has expanded and you are no longer sure whether its technology practices have kept pace, that uncertainty may be a useful place to begin the conversation.
The first step is not necessarily buying something new.
It may simply be understanding what your business has become and whether the systems protecting it have grown with it.