Who Really Has Access to Your Business Information?


An employee needs access to a new business application. Someone from IT creates the account, assigns the permissions, and the employee gets back to work.
A few months later, that employee moves into another role. Their new responsibilities require access to different systems, but nobody thinks to remove the permissions they no longer need.
Meanwhile, an outside consultant has been given access to a shared folder. A maintenance company has remote access to a system it occasionally services. A former employee's account may still exist in an application that nobody remembers to check.
None of these arrangements necessarily began as a bad decision.
Each may have been a reasonable response to a legitimate business need.
The difficulty is that access tends to accumulate much more easily than it disappears.
Over time, a business can reach a point where nobody has a complete answer to a surprisingly simple question:
Who can actually access our business information and systems today?
The problem isn't always unauthorized access
When business owners think about protecting company information, they often think about keeping outsiders from getting in.
That matters, but it is only part of the picture.
Some of the most difficult access questions involve people who were legitimately granted permission.
An employee needed access to financial information for a temporary assignment. A contractor required administrative privileges to complete a project. A software provider needed remote connectivity to troubleshoot an application.
The original authorization may have been entirely appropriate.
But circumstances change.
Projects end. Employees change responsibilities. Business relationships evolve. Applications are replaced. Outside providers change personnel.
The question is no longer simply whether access was authorized when it was created.
The question is whether that access is still appropriate today.
For a small or medium-size business, this can be particularly challenging because access decisions are often spread across several people.
An office manager may approve access to a business application. A department manager may control shared files. An IT provider may administer the network. An outside vendor may manage its own support accounts.
Everyone may be doing their part, yet nobody has the complete picture.
Access extends far beyond employee usernames
A useful starting point is recognizing how many different ways people and systems can access business information.
There are the obvious accounts: employees signing into email, accounting software, customer management systems, and shared documents.
Then there are the less visible arrangements.
An outside accountant may have access to financial records. A maintenance provider may connect remotely to equipment. A consultant may use a shared administrative account. A software integration may exchange information automatically between two applications.
Some systems use individual accounts. Others rely on shared credentials, application tokens, or automated service accounts.
These arrangements serve different purposes, but they create a common management question:
Who is responsible for deciding whether this access should continue?
A business doesn't necessarily need an elaborate system to begin answering that question.
It needs to identify its important systems, understand who uses them, and establish ownership of access decisions.
That ownership is often more valuable than another spreadsheet containing usernames that nobody regularly reviews.
Who decides what someone should be allowed to do?
Consider a new employee joining the accounting department.
IT can create an account, but IT may not know whether that person should approve payments, modify supplier banking information, or simply view financial reports.
Those are business decisions.
The accounting manager understands the responsibilities. The business owner may need to approve certain privileges. IT can then implement the appropriate permissions.
When these responsibilities are unclear, access decisions can become informal.
Someone asks for permission because they need to finish a task. Another employee already has access, so copying their permissions seems convenient.
The immediate problem is solved.
But copying access from one person to another can also copy permissions that are unnecessary.
A more manageable approach separates three responsibilities:
- Business authorization: Someone responsible for the work determines what access is justified.
- Technical implementation: The appropriate administrator provides access through the supported controls.
- Ongoing ownership: Someone remains accountable for reviewing that access as responsibilities change.
This doesn't require a committee for every routine request.
It requires a process that people understand and can follow without unnecessary delays.
When outside partners need access to your business
External access deserves particular attention because it often crosses organizational boundaries.
A refrigeration maintenance company, for example, may need remote connectivity to equipment at a customer's location.
That access can be essential.
Without it, diagnosing a problem might require an on-site visit, increasing delays and operational costs.
But a legitimate maintenance relationship introduces questions that are easy to overlook.
Who at the maintenance company can connect? Does the business know when access is being used? Is access limited to the equipment involved? What happens when the maintenance contract ends?
These questions become especially important when remote connectivity reaches systems that support daily operations.
The previously discussed French supermarket refrigeration incident provides a useful related example of why third-party maintenance access deserves attention.
The broader lesson is not that businesses should stop working with outside providers.
It is that authorized external access should remain visible, purposeful, and manageable throughout the relationship.
Where practical, businesses can use individually assigned accounts, appropriately limited permissions, multifactor authentication, controlled remote connectivity, and access that is enabled only when needed.
The exact controls depend on the equipment, applications, and support arrangements involved.
What matters is that convenience does not quietly become permanent, unmanaged access.
Making access easier without losing control
There is another side to this discussion that businesses sometimes overlook.
Employees and partners need to work.
If every access request requires multiple emails, manual password exchanges, and long waits for someone in IT, people naturally look for shortcuts.
They may share credentials through messages, reuse an existing account, or store passwords somewhere convenient.
The answer cannot simply be to make access more difficult.
A better process should make approved access easier while reducing unnecessary exposure.
For example, centrally managed business credentials can help employees locate approved logins without searching through old emails or asking colleagues for passwords.
Supported secure-sharing arrangements can allow an authorized employee or partner to sign in without the password being displayed during normal use.
That can make collaboration more practical, particularly when several people need to work with the same business application.
However, concealed password sharing is not a guarantee that a determined recipient can never obtain the credential.
And withdrawing permission to use a shared credential is not necessarily the same as terminating an active application session or invalidating a password that may already be known.
Those distinctions matter when designing a reliable access process.
The objective is not simply to distribute credentials more securely.
It is to help authorized people perform their work while preserving the business's ability to manage and withdraw access.
Access should have a beginning, a purpose, and an end
One useful way to organize access management is to follow its entire lifecycle.
Authorize
Identify who needs access, what they need to accomplish, and who approves it.
The approval should come from someone who understands the business responsibility, not solely from whoever administers the technology.
Enable
Provide the appropriate access through a supported, controlled method.
Where feasible, use named accounts, limited permissions, and centrally managed business credentials rather than informal password sharing.
Use
Make sure the person can complete the intended work.
Controls that prevent legitimate work may encourage people to bypass the process.
Review
Reconsider permissions when employees change roles, projects end, vendors change, or important systems are modified.
Higher-risk access, such as administrative privileges and external remote connectivity, may deserve more frequent attention.
Withdraw
Remove access when it is no longer justified.
Then verify the removal at the relevant systems.
This final step is particularly important because removing a person from one management system does not necessarily remove every way they can still connect.
Why employee departures are a revealing test
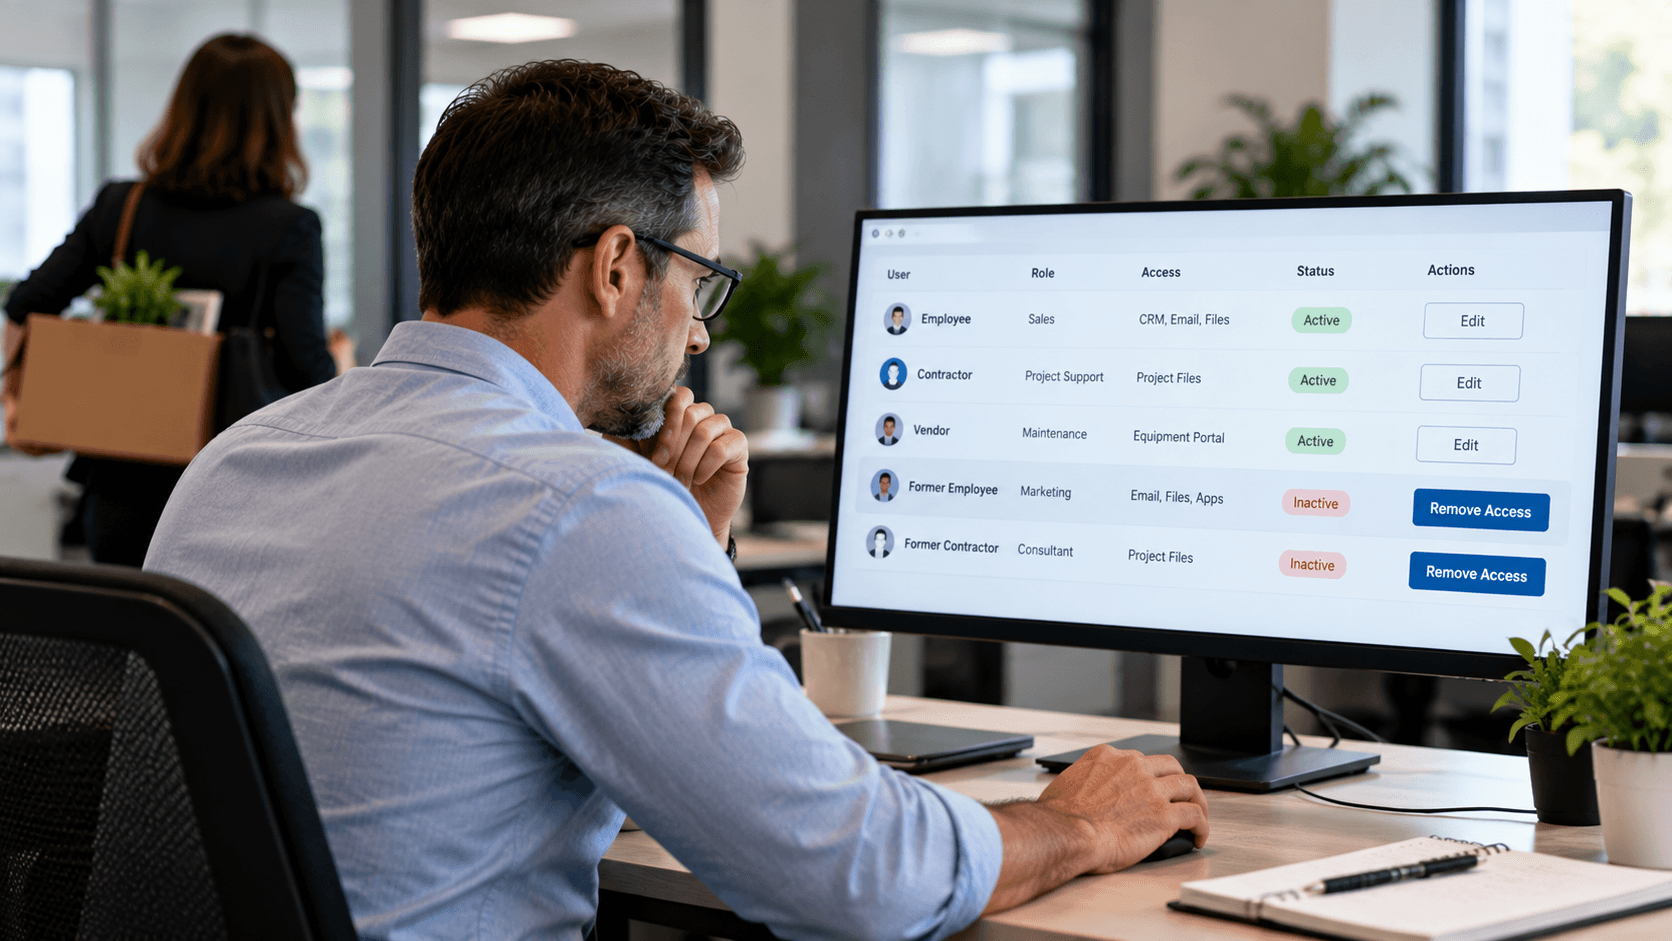
An employee leaving the company provides a practical opportunity to evaluate how well access is managed.
Disabling the employee's primary company account is an important step.
But what about the accounting application with separate credentials?
What about the external supplier portal?
What about a shared administrative password the employee previously knew?
What about active sessions on independently managed services?
A central identity system can simplify account administration and automate removal from supported connected applications.
But businesses should not assume that disabling one account automatically closes every session, revokes every token, or removes access to every independently managed service.
Shared credentials may need to be changed. Separately managed accounts may need to be disabled. Business-owned information and credentials must remain available to authorized employees.
This is why offboarding works best when the business has already documented which systems employees use and who is responsible for them.
Trying to reconstruct that information after someone leaves is much harder.
The same principle applies when a contractor completes a project or an outside maintenance relationship ends.
What should a smaller business review first?
It may be unrealistic to document every permission across every application immediately.
That does not mean the business has to wait until it can undertake a comprehensive project.
A practical first review could concentrate on the systems whose loss, misuse, or disruption would have the greatest operational consequences.
Start with the systems used for financial transactions, customer information, important business documents, core operations, and remote administration.
For each one, try to answer a few questions:
- Who is responsible for approving access?
- Which employees and outside parties currently have access?
- Are any shared or administrative credentials involved?
- How are new permissions granted and recorded?
- What triggers an access review?
- How would the business verify that access was removed?
Some answers may be incomplete.
That is useful information in itself.
An unidentified system owner, an unexplained administrative account, or a vendor connection without a clear purpose gives the business something specific to investigate.
The first objective is visibility, not perfection.
How do you know the process is improving?
A new policy does not necessarily mean access is better controlled.
The more useful evidence comes from ordinary business activities.
Can a new employee receive the appropriate access without borrowing someone else's credentials?
When someone changes roles, are old permissions reconsidered?
Can the business identify the outside providers with access to important systems?
When a contractor finishes work, can the responsible person confirm which permissions were withdrawn?
Can the company retain ownership of its business credentials and information when an employee or provider leaves?
These are practical measures of whether access management supports the organization.
They also reveal whether the process is manageable enough to become part of normal operations.
A complicated system that everyone avoids may provide less real control than a simpler process that people consistently follow.
The question worth asking before something goes wrong
Most businesses do not deliberately create uncontrolled access.
They make individual decisions to keep work moving.
A new employee needs an account. A supplier needs remote support. A consultant needs temporary access. Someone shares a credential to solve an immediate problem.
Each decision may make sense at the time.
The challenge is remembering that permissions continue to exist after the original task has been completed.
Over time, those decisions become part of the company's technology environment.
The business should be able to understand and manage them.
Knowing who has access is not about distrusting employees or making collaboration difficult.
It is about maintaining control over information and systems that the business depends on.
And perhaps the most useful question is not whether everyone currently has the access they need.
It is this:
If someone no longer needed access tomorrow, would you know everywhere to remove it, and how to confirm that it was gone?
If that question is difficult to answer, it may be time to review how access is granted, shared, monitored, and withdrawn.
Nivo 5 helps businesses bring structure to technology administration, business credentials, and access management. If your organization is unsure who can reach its important systems, a conversation about your current environment can be a practical place to begin.